CfbModeTransform Class
Definition
- Namespace
- Bodu.Security.Cryptography
- Assembly
- Bodu.Security.Cryptography.dll
- Package
- Bodu.Security.Cryptography 1.3.0
- Source
- CfbModeTransform.cs
Applies the Cipher Feedback (CFB) mode transformation to an underlying IBlockCipher, turning it into a self-synchronizing stream cipher.
public sealed class CfbModeTransform : IBlockCipherModeTransform, IDisposable- Inheritance
-
CfbModeTransform
- Implements
- Inherited Members
- Extension Methods
Examples
using System.Security.Cryptography;
using Bodu.Security.Cryptography;

// Most callers set BlockMode = CipherModeKind.CFB on a SymmetricAlgorithm wrapper instead of using this directly.
using IBlockCipher cipher = new AesBlockCipher(key);
byte[] iv = RandomNumberGenerator.GetBytes(cipher.BlockSize / 8);
IBlockCipherModeTransform cfb = new CfbModeTransform(cipher, iv);
byte[] ciphertext = new byte[paddedPlaintext.Length]; // a whole number of blocks
int written = cfb.Transform(paddedPlaintext, ciphertext, encrypt: true);
Remarks
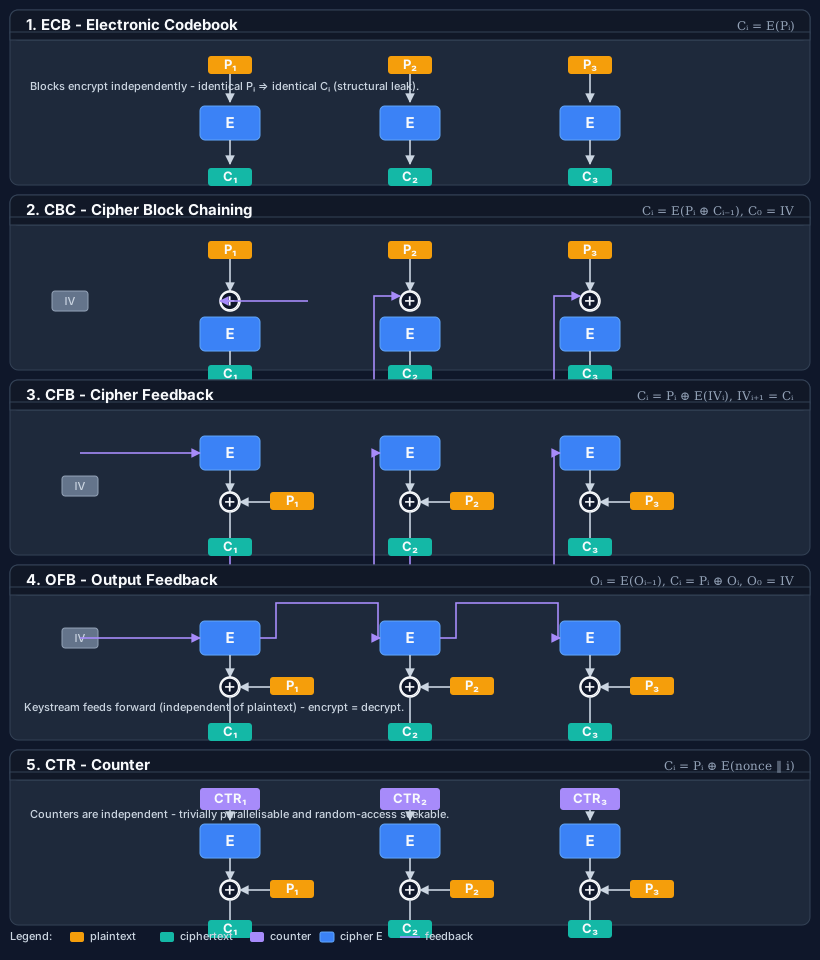
Both directions use the cipher's encryption primitive: encryption computes Cᵢ = Pᵢ ⊕ E(IVᵢ) and decryption
Pᵢ = Cᵢ ⊕ E(IVᵢ), with IV₀ supplied by the caller and IVᵢ₊₁ = Cᵢ for subsequent blocks. See
panel 3 of the diagram above: the dashed feedback lines carry ciphertext blocks back into the next cipher
input - the cipher runs the same direction (encrypt) for both encryption and decryption, and the plaintext simply
XORs into or out of the resulting keystream.
The initialization vector must equal the cipher block size in length and should be unique and unpredictable per message under a given key.
When to use CFB. Pick CFB only for interoperability with legacy formats - it was the stream-cipher mode of choice in PGP / OpenPGP and certain disk-encryption layouts. This is full-block CFB: its input must be a whole number of blocks, so it needs padding exactly as CbcModeTransform does. It inherits CBC's lack of authentication and adds bit-flip propagation across multiple blocks. For new code prefer CtrModeTransform for stream-cipher behavior, or an AEAD mode (GcmModeTransform, EaxModeTransform) for authenticated encryption.
CFB encryption is sequential at the block level: each ciphertext block must be produced before the next can be computed. Decryption is not, because every feedback input is already in the ciphertext, so runs of blocks are processed with one multi-block EncryptBlocks(ReadOnlySpan<byte>, Span<byte>) call.
Constructors
CfbModeTransform(IBlockCipher, byte[])
Initializes a new instance of the CfbModeTransform class with the specified cipher and initialization vector.
public CfbModeTransform(IBlockCipher cipher, byte[] iv)Parameters
cipherIBlockCipherThe block cipher over which CFB is applied.
ivbyte[]The initialization vector used as the feedback register for the first block. A defensive copy is taken.
Exceptions
- ArgumentNullException
Thrown if
cipherorivis null.- ArgumentException
Thrown if the length of
ivdoes not equal the block size ofcipher.
Methods
Dispose()
Releases the resources used by this instance and zeroes the running feedback register so that key-equivalent state does not linger in memory after disposal. The underlying IBlockCipher is not disposed by this type - ownership remains with the caller.
public void Dispose()Remarks
Idempotent.
Transform(ReadOnlySpan<byte>, Span<byte>, bool)
Transforms input under the mode's chaining strategy and writes the result to
output.
public int Transform(ReadOnlySpan<byte> input, Span<byte> output, bool encrypt)Parameters
inputReadOnlySpan<byte>The input data to transform.
outputSpan<byte>The destination span. Its length must be greater than or equal to the length of
input.encryptbool
Returns
- int
The number of bytes written to
output.
Remarks
The length rule depends on the mode: ECB, CBC, CFB, OFB, and XTS accept a whole number of blocks, zero included; CtrModeTransform accepts any length; CtsModeTransform accepts any length of at least one block.
Exceptions
- ArgumentException
Thrown when
outputis shorter thaninput, or, for CtsModeTransform, wheninputis shorter than one block.- CryptographicException
Thrown when the mode accepts only whole blocks and the length of
inputis not a multiple of the block size, or wheninputandoutputpartially overlap.- ObjectDisposedException
Thrown when the transform has been disposed.
Applies to
| Product | Versions |
|---|---|
| .NET | 8, 10 |